AI solutions
What we do
Services
Experts in
How we work
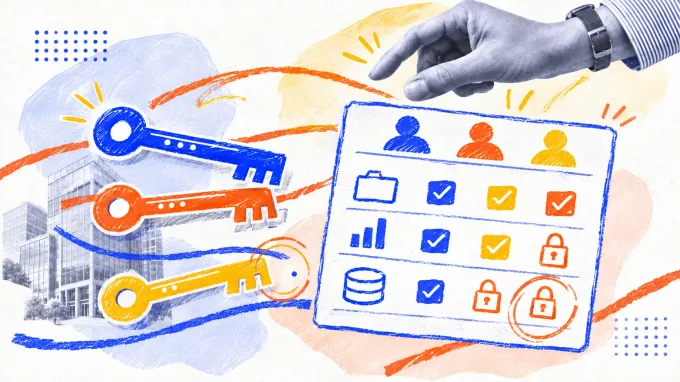
A B2B account works like an apartment building. Everyone lives under one roof, and each tenant has keys to their own apartment and a few shared spaces. Corporate clients expect the same setup from your product. Branch managers should see only their teams, finance staff should manage invoices, and a contractor should open and edit one project.
If your product offers only two options, admin and user, it can’t serve any of these needs. Give everyone admin access, and you create risk. Keep them as users, and they can’t do their jobs. The fix is a well-designed set of SaaS roles and permissions: rules that define which organization a person belongs to, which actions they can take, and which resources those actions cover.
This guide will walk you through the whole process.
Here, we'll explain how to define roles and permissions in SaaS, choose an authorization model, and test the result. Our team brings experience with role- and team-based access in business applications. We will use a clearly labeled example to connect product decisions with implementation, then show what this work should deliver.
Authentication establishes who is signing in. Authorization decides what that person can do. Effective SaaS access control depends on keeping several related concepts distinct.
An identity represents a person or service. A membership connects that identity to an organization. A role bundles permissions for a function, such as billing administration. A permission describes an action on a resource: viewing an invoice, inviting a member, or exporting a report. Scope limits where that permission applies, such as one organization, branch, or project.
Consider Maya, a manager in the North branch. Her membership belongs to Acme Operations. Her role allows project updates, and her assignment limits that authority to North. The same identity might have a different membership elsewhere. A single global role on Maya's user record cannot describe both situations accurately.
The practical distinction in roles vs permissions is that your application checks the action, while administrators manage understandable bundles. Renaming a role should not require rewriting those checks.
Subscription entitlements describe capabilities granted through a plan or contract. Acme may have purchased advanced reporting. That does not mean every employee can export financial data.
For Maya's export request, the application must establish that Acme has the reporting capability, Maya has the export permission, and the requested data falls within her scope. Relevant restrictions still apply even when the feature is paid for. Treating an enterprise plan as a user role would collapse these separate decisions and grant access too broadly.
Start designing SaaS user roles by collecting workflows, rather than asking customers which role names they want. What does a branch manager need to change? Who can invite a contractor? Does viewing a report also permit downloading its underlying data?
Our illustrative example is a B2B operations platform with organizations, branches, projects, invoices, and external contractors. Acme has North and South branches. Managers work within a branch, finance operates across the billing account, and contractors receive project assignments. This is a teaching example, not a Clockwise client configuration.
When defining access rules for SaaS applications, name sensitive actions separately. Reading an invoice, changing a payment method, and granting billing access are different permissions. Likewise, editing a project need not include deleting it or inviting other people. Split permissions when customers need different authority or the actions carry different risks. Avoid adding separate permissions for every minor screen interaction.
The following SaaS permission matrix describes one possible policy. Its B2B SaaS user roles reflect job responsibilities, with scope recorded alongside the action.
| Action | Owner | Branch manager | Billing manager | Contractor |
| Manage memberships | Organization | Own branch | No | No |
| Edit projects | Explicit grant only | Own branch | No | Assigned projects |
| View invoices | Explicit grant only | No | Billing account | No |
| Change payment method | Explicit grant only | No | Billing account | No |
| Export project reports | Explicit grant only | Own branch | No | No |
This example deliberately separates organizational ownership from unrestricted access to business data. Your policy may differ. The important point is to agree on that behavior rather than assume the owner means everything.
Turn each matrix row into examples with named resources. Maya can update a North project because her role and branch assignment allow it. She cannot update a South project, even through a direct URL. Both outcomes belong in acceptance criteria.
Record unresolved questions next to the matrix. For example, should a manager see archived projects after changing branches? Product owners must settle that policy before engineering can implement it consistently. The matrix becomes a shared reference for development, customer documentation, and QA.
Review your account structure and permission model before adding more exceptions. Our SaaS development services can connect these requirements with architecture, implementation, and testing.
Role-based access control for SaaS works well when responsibilities form recognizable bundles. Billing managers handle invoices. Branch managers maintain branch operations. Contractors work on assigned projects. Customers can understand these roles, and your team can review what each one permits.
Each role assignment should include its scope. You do not need separate role definitions named North Manager and South Manager when both have identical permissions. Assign the same manager role at different branches. Creating a new role for every location, project, and exception leads to role explosion.
Choosing an access-control model for SaaS starts with rules your product must express. A library or managed platform should support those rules, rather than determine them by default. Keep the policy understandable enough that a customer administrator can explain a user's access.
Some decisions need more than a job function. A manager might approve expenses only below an agreed limit. That decision uses attributes of the person and transaction. A contractor might edit a project only because an assignment connects them to that resource. That decision uses a relationship.
The useful comparison in RBAC vs ABAC vs ReBAC is therefore the information required for a decision. Roles describe functions; attributes describe relevant properties and context; relationships describe connections such as membership, ownership, and sharing. They can work together.
Simple scoped assignments do not automatically require a graph service. A small product may express the same relationship through its own data model and shared authorization module. More complex inheritance and collaboration can justify a dedicated engine. Evaluate representative rules, permission reviews, and operational requirements before choosing the implementation. Adding expressive power also adds policies your team must maintain and test.
Store identity independently from the access granted through a membership. In our example, Maya is a North manager at Acme and a contractor on one project at Beacon. Acme's membership and assignments must not influence requests made within Beacon.
The conceptual model below separates those responsibilities. Membership establishes participation in an organization. An assignment combines that membership with a role and scope. Resources carry their own organizational and structural context.
[INSERT: conceptual model diagram]
Organization-scoped roles prevent a global admin flag from following a person everywhere. For finer control, resource-level permissions can attach to a branch or project within that organization. Each decision must connect the requested resource to the applicable assignment; knowing the user's selected organization alone is insufficient.
Treat this as a conceptual model, not a mandatory database schema. A provider may represent memberships, groups, and assignments differently. Whatever the storage, SaaS roles and permissions must preserve the same product boundaries. Keep assignment identifiers stable and distinguish display names from policy identifiers. That lets customer administrators rename a role without changing the rules that reference it.
Tenant-scoped role-based access control still needs explicit rules for inheritance. Does branch access cover every project beneath it? Can a confidential project block inherited access? Can a direct assignment add authority that a broader role lacks?
Choose and document the answers. If permissions combine additively, say so. If an explicit restriction overrides a grant, define its precedence. A role called viewer does not inherently cancel edit access obtained through another valid assignment.
Moving a project from North to South also changes its context. Decide which inherited permissions change and whether direct contractor assignments remain. Check the operation that moves the project, as well as access afterward, so users cannot move resources to gain authority indirectly.
These rules build on multi-tenant architecture, which establishes customer boundaries. Within those boundaries, the access model determines which members can act on which resources.
SaaS custom roles let customers assemble supported permissions into job functions you did not anticipate. Keep them within an organization and expose only permissions that customers are allowed to configure. New permissions should not silently appear in existing custom roles through a broad wildcard.
Managing roles and permissions in a SaaS product requires separating administration actions. Creating a role, editing its permissions, assigning it, and expanding its scope are different powers. A person who can export reports does not necessarily have authority to grant export access to others.
For delegated administration, define an explicit grant ceiling. A North manager may invite people into the North and assign approved branch roles. They cannot create an organization-wide role or add billing authority. Validate the proposed role contents and target scope on the server, including edits to a role that is already assigned.
An acceptance criterion could read: changing a branch role to include organization-level membership management is rejected, and existing assignments remain unchanged. This tests the escalation path directly.
SaaS access control must cover administrative edge cases. Transferring ownership needs an eligible recipient, an authorized initiator, and a defined effective time. Removing or demoting the last required owner should be blocked unless a controlled recovery process applies.
For contractors, define an expiry date or review point and the exact resources covered. Expiration must affect enforcement, not merely add a warning in the interface. Decide who maintains scheduled work and owned records after departure.
Support access is another privileged workflow. If staff can act within a customer account, distinguish the support operator from the represented user, limit the session, and record sensitive actions. Customer approval requirements should follow your product policy. An unrestricted support bypass undermines the boundaries you built for customer administrators.
Frontend controls help users understand available actions. They cannot enforce SaaS access control by themselves. A caller can bypass the interface and submit an API request directly, including a different project ID or organization identifier.
Use server-side authorization to establish trusted identity, current membership, resource context, and the applicable rule. The backend must verify how a resource belongs to an organization. A client-supplied identifier is a request to inspect, not proof of access.
Conceptually, object-level authorization for a project update follows this sequence. This pseudocode illustrates the checks; actual transaction and consistency handling depends on the application.
identity = verify_credentials(request)


membership = require_active_membership(identity, organization)


project = load_project_with_verified_tenant_context(project_id, organization)


require_permission(membership, "project:update", project)


update_project_with_consistency_checks(project, changes)
OWASP's authorization guidance recommends denying access by default and checking permissions on every request. Access control for SaaS applications needs consistent enforcement points so a new endpoint does not accidentally inherit permissive behavior.
Enforcing role-based permissions in SaaS also means controlling data discovery. A protected project detail endpoint is insufficient if search returns confidential project names. Filter lists, counts, reports, and exports to the permitted resources before returning results. Paginating a broad query and hiding unauthorized rows afterward can produce incorrect pages and leak information through totals.
Bulk operations need an agreed policy when only some items are authorized. Either reject the request or return clearly defined partial results. Do not silently apply actions outside the caller's scope.
Background jobs need an explicit authority model. A user-requested export can carry the initiating identity, organization, requested scope, and relevant audit context. Check authorization when accepting the request and again at execution or result release where the policy requires current access. Do not copy a browser session token into a long-lived job and assume it remains valid indefinitely.
Scheduled organization reports may instead run under a service identity with approved permissions. That is a separate product workflow. Defining who authorizes it and who may retrieve its output avoids treating every automated task as an administrator. For expiring download links, account for the interval during which a previously issued link remains usable. A later role check cannot revoke a link that already grants independent access unless the delivery design supports that control.
Updating user permissions in SaaS involves more than writing a new role assignment. A signed token may still contain old permissions, and a cached decision may outlive the membership that produced it. Define the acceptable delay between a change and enforcement, especially for removal or administrative demotion.
Microsoft's SaaS identity guidance notes that token claims refresh when tokens are reissued, which can delay permission changes. Signature validation confirms token integrity; it does not prove that its permission claims remain current.
Options include current-state checks, short token lifetimes, session revocation, policy versions, and targeted invalidation. Select them according to the required freshness and operating cost. Authorization cache invalidation must cover policy edits, assignment changes, and resource context. A cache key also needs the relevant tenant, action, and resource information.
Consider permission revocation during Maya's export. At 10:00, the request passes its checks. At 10:01, she loses the manager assignment. At 10:02, the worker begins. Under our illustrative policy, the worker checks current authority and stops the user-requested export. If it had already finished, the download endpoint would still reject her request.
Other products may retain approved scheduled reports under a service identity. Document the distinction so background behavior is intentional.
Maintaining consistent SaaS authorization also requires ownership of changes. Identify whether memberships come from the application or a customer directory, how groups map to roles, and whether local overrides are allowed. Reconcile missed updates and reject older updates where ordering information permits. Removing one organization's membership must not erase legitimate access to another organization. Test both removal and continued access using the same identity.
The build vs buy authorization decision comes after the permission model. A platform that stores roles cannot resolve an undefined branch hierarchy or decide whether contractors may export reports.
Compare implementation approaches against your actual rules. Centralized logic can be a shared module inside a monolith; it does not necessarily require a separate service. An authorization policy engine becomes useful when policy complexity, multiple services, or operational ownership justify it.
| Approach | Suitable conditions | Responsibility your team keeps |
| Application module | Limited rules in one application | Consistent checks, policy changes, tests |
| Library or policy engine | Rules need a formal model or shared evaluation | Hosting where applicable, integration, policy data |
| Managed service | Supported model and vendor operations fit | Resource synchronization, enforcement, failure handling |
When evaluating RBAC for SaaS, test tenant-scoped assignments, multiple roles, custom-role restrictions, and revocation behavior. If relationships matter, test inheritance and resource moves too. A successful demo of a single allowed decision does not establish fit.
Ask how the solution supports listing accessible resources. Individual permission checks may work well while an unfiltered list requires expensive per-record calls. Measure expected authorization volume and latency on representative workflows.
SaaS access control also needs a defined response to timeouts or unavailable policy data. Avoid turning failures into unrestricted access. If previously validated decisions can be cached temporarily, specify the actions, freshness limits, and revocation implications. Sensitive writes may require a stricter response than low-risk reads. Document the fallback and test it under an actual timeout, rather than relying on the normal success path.
The AWS authorization guide distinguishes policy decision points from enforcement points. That distinction helps you assign responsibility without assuming one deployment pattern fits every product. Include vendor fees, policy maintenance, synchronization, and a future exit path in the evaluation.
SaaS roles and permissions are ready for release when the agreed rules survive real application paths. Convert the matrix into authorization test cases that exercise backend operations with representative users, memberships, and resources. Checking whether a button appears is only part of the interface test.
For each allowed action, create a nearby denied case: the wrong branch, another organization, an expired assignment, or an unauthorized role. Include combinations of roles and direct assignments, because effective permissions may differ from one role's definition.
| Scenario | Expected decision | Evidence |
| Maya edits a North project | Allow; update saved | API result and stored change |
| Maya submits a South project ID | Deny; no update | API result and unchanged record |
| Billing manager exports project data | Deny | Export request rejected |
| Contractor searches other projects | No unauthorized results | List, totals, and search checks |
| Manager expands a role beyond grant ceiling | Deny; role unchanged | Policy record and audit event |
| Revoked manager retrieves an export | Deny under agreed policy | Download rejected |
Testing role-based access control in SaaS should also cover permission changes while a request or job is in progress. Confirm that consistency checks prevent an operation from using a resource's outdated scope where that would break the policy.
Test ownership transfer, removal of the last required owner, resource moves, custom-role edits, and access through service identities. These paths can expose gaps even when ordinary reads and writes work. Cross-tenant negative tests remain necessary alongside within-tenant checks.
A permission audit trail should explain sensitive administrative changes: actor, organization, target, action, time, and outcome. Include the policy version or assignment context when useful for investigation. Avoid recording credentials or unnecessary sensitive payloads. Choose decision logging based on risk and volume rather than promising to store every read forever.
Authorization testing belongs within broader SaaS security. Keep regression cases for previously fixed access bugs, and make policy changes subject to review so new permissions do not bypass the release process.
Redesigning roles and permissions in an existing SaaS product starts with discovering actual behavior. Inventory checks in APIs, jobs, reports, support tools, and integrations. Interview people who handle customer exceptions; some permissions exist only as manual procedures.
When introducing RBAC for SaaS, map old users to memberships, assignments, and scopes before switching enforcement. An old admin flag may combine billing, user management, and data access. Splitting it requires a policy decision about which users retain each power. Technical equivalence is not always the desired outcome.
Shadow authorization checks let the new evaluator calculate decisions while the old implementation still controls access. Compare outcomes with enough context to explain differences. However, a match does not prove safety: the old system may already allow too much, and unobserved workflows still need tests.
Migrating SaaS authorization rules needs a staged plan: backfill memberships, validate assignments, explain changes to customer admins, and enable selected organizations. Classify discrepancies as intentional restrictions, intended grants, missing data, or defects. Do not let unexplained differences accumulate behind a rollout percentage.
An illustrative release gate is that critical workflows pass, assignment mappings are reviewed, and no unintended grants remain in the evaluated scope. Monitor denied actions and support reports after release without automatically restoring broader access.
Define recovery before changing data. A feature flag may restore an old evaluator, but it cannot recreate deleted assignments or undo ownership transfers. Preserve the necessary history and test recovery procedures.
Implementation cost depends on these migration requirements as much as on the policy checks. Include discovery, customer administration, integrations, QA, and ongoing maintenance when planning the development budget. A narrow estimate for replacing conditional statements can miss most of the work.
Designing access control for a B2B SaaS product requires product analysis as well as engineering. We can help translate customer workflows into an account model, permission matrix, implementation scope, and acceptance criteria. The goal is to agree on what the system should allow before choosing how to enforce it.
Our product discovery services include a roles and permissions matrix among the available deliverables. For an existing product, that work can also identify current behavior, conflicting assumptions, and migration dependencies. The exact deliverables should match the product's needs.
In our work with Foresolutions, we implemented access to functionality and data according to user roles and their department or team. The product served drivers, operators, administrators, and managers. During discovery, we also investigated roles and their assignment conditions to support user importing. The example shows why role definitions and organizational scope need to be designed together.
SaaS access management development should carry those decisions into APIs, administration screens, automated work, and tests. Keeping discovery and implementation connected helps preserve the reasons behind the rules. It also makes responsibilities clearer: who approves policy, implements checks, validates migration, and maintains the result. Bring representative customer requests and existing restrictions so we can discuss the scope your product actually needs.
Plan roles and permissions for your SaaS product around the workflows customers need and the boundaries you must preserve. Start with representative users, actions, resources, and denied scenarios. Then agree on delegation, change propagation, and release criteria.
Clockwise can help assess the current account structure and carry an agreed model into implementation and QA. Share your role definitions, difficult customer requests, and known limitations. We can discuss gaps, dependencies, and options before you commit to a broader development scope.